0%
💸 Launch Offer for the first 50 founders: Save at least $132.

Get Vibe44. Skip the hard part.
And, Ship in a Weekend!

Build Smart. Ship Faster.
Join the Cool Founders.

Deep dives, guides, and strategic insights for independent founders, developers, and AI engineers looking to ship products, SaaS, and AI-powered applications.

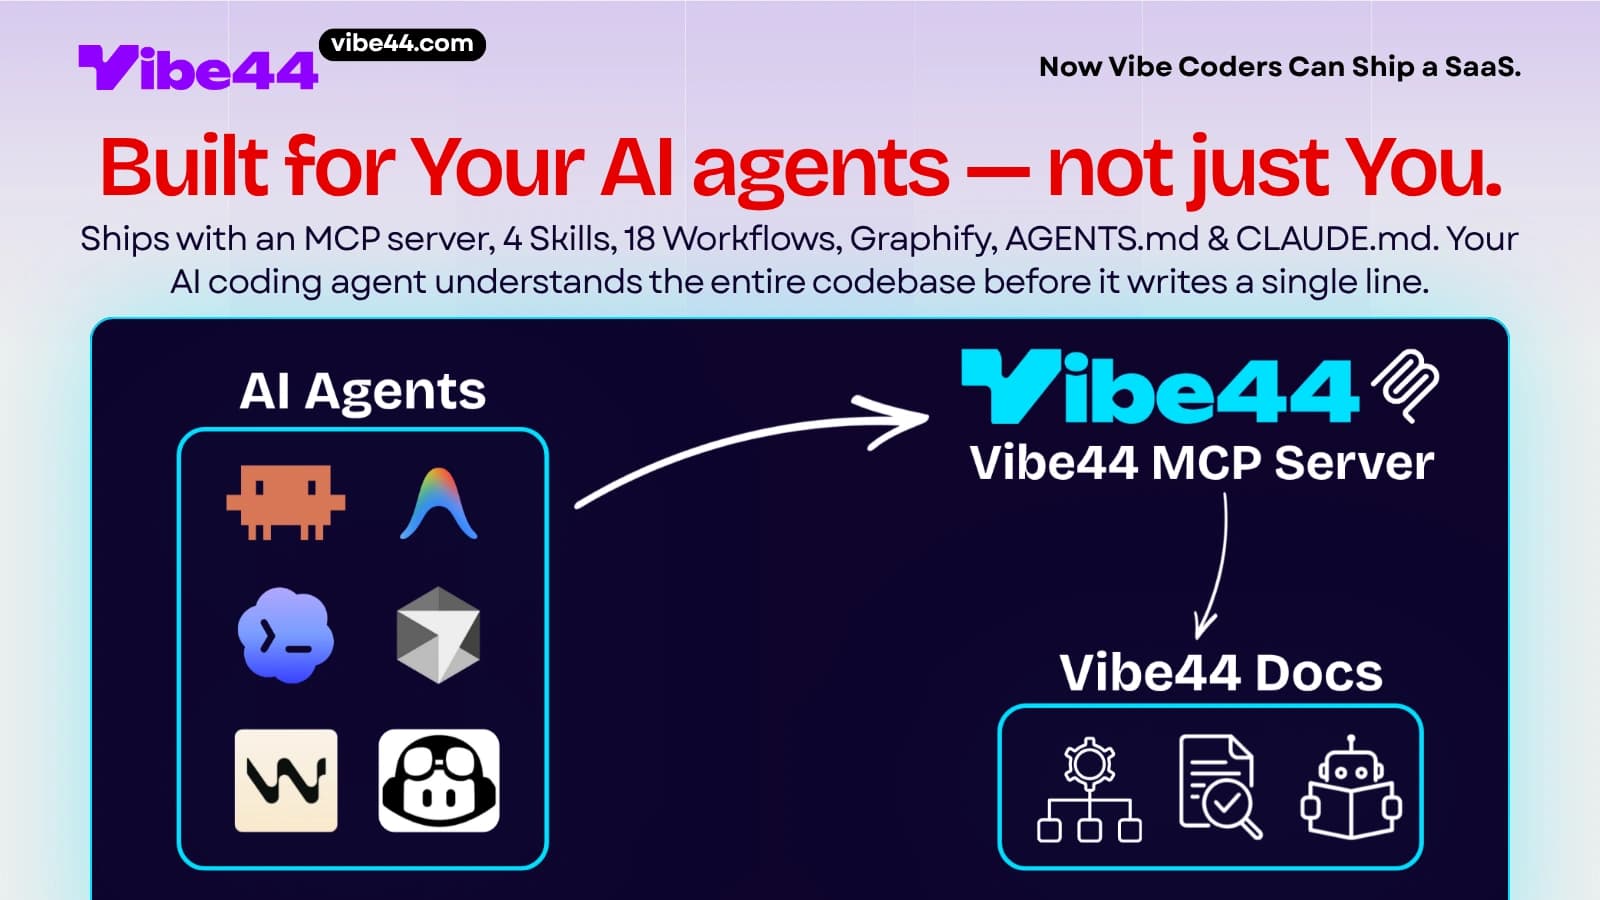
A diagram showing how Vibe44 is built for AI agents, depicting various AI agent logos pointing to a Vibe44 MCP Server, which in turn connects to Vibe44 documentation resources.
★ FeaturedAI & Agents

From Idea to Paying Users in a Weekend — An AI-Agent-Driven Building System.

You can build SaaS with AI in a weekend, but only if your agent starts on a real foundation. Vibe44 ships that foundation — AGENTS.md + CLAUDE.md, the Graphify Context Engine (up to 71.5x token cost reduction), a public docs MCP server, and 900 unit tests plus 9 E2E suites that catch agent mistakes before prod.

Alap Putatunda

Written by AI &

Alap Putatunda

June 11, 2026Read Full Article
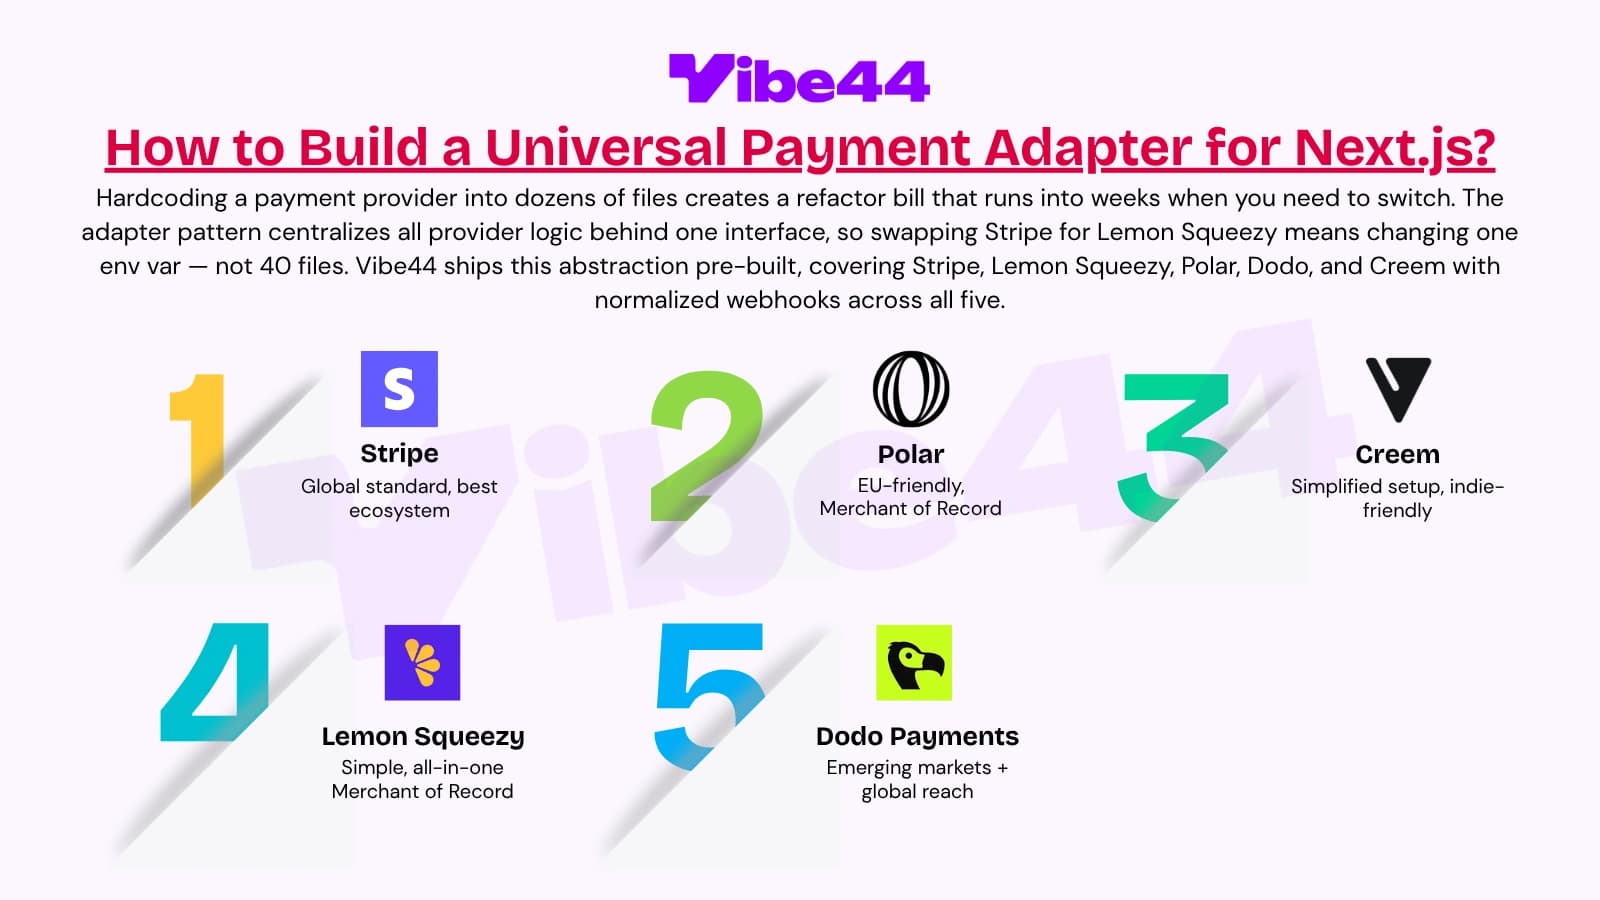
A visual list numbering 1 to 5, displaying logos for five payment providers: Stripe, Polar, Creem, Lemon Squeezy, and Dodo Payments.
★ FeaturedPayments & Production

Stop Hardcoding Stripe! How to Build a Universal Payment Adapter for Next.js?

Hardcoding a payment provider into dozens of files creates a refactor bill that runs into weeks when you need to switch. The adapter pattern centralizes all provider logic behind one interface, so swapping Stripe for Lemon Squeezy means changing one env var — not 40 files. Vibe44 ships this abstraction pre-built, covering Stripe, Lemon Squeezy, Polar, Dodo, and Creem with normalized webhooks across all five.
Alap Putatunda

Written by AI &

Alap Putatunda

June 7, 2026Read Full Article
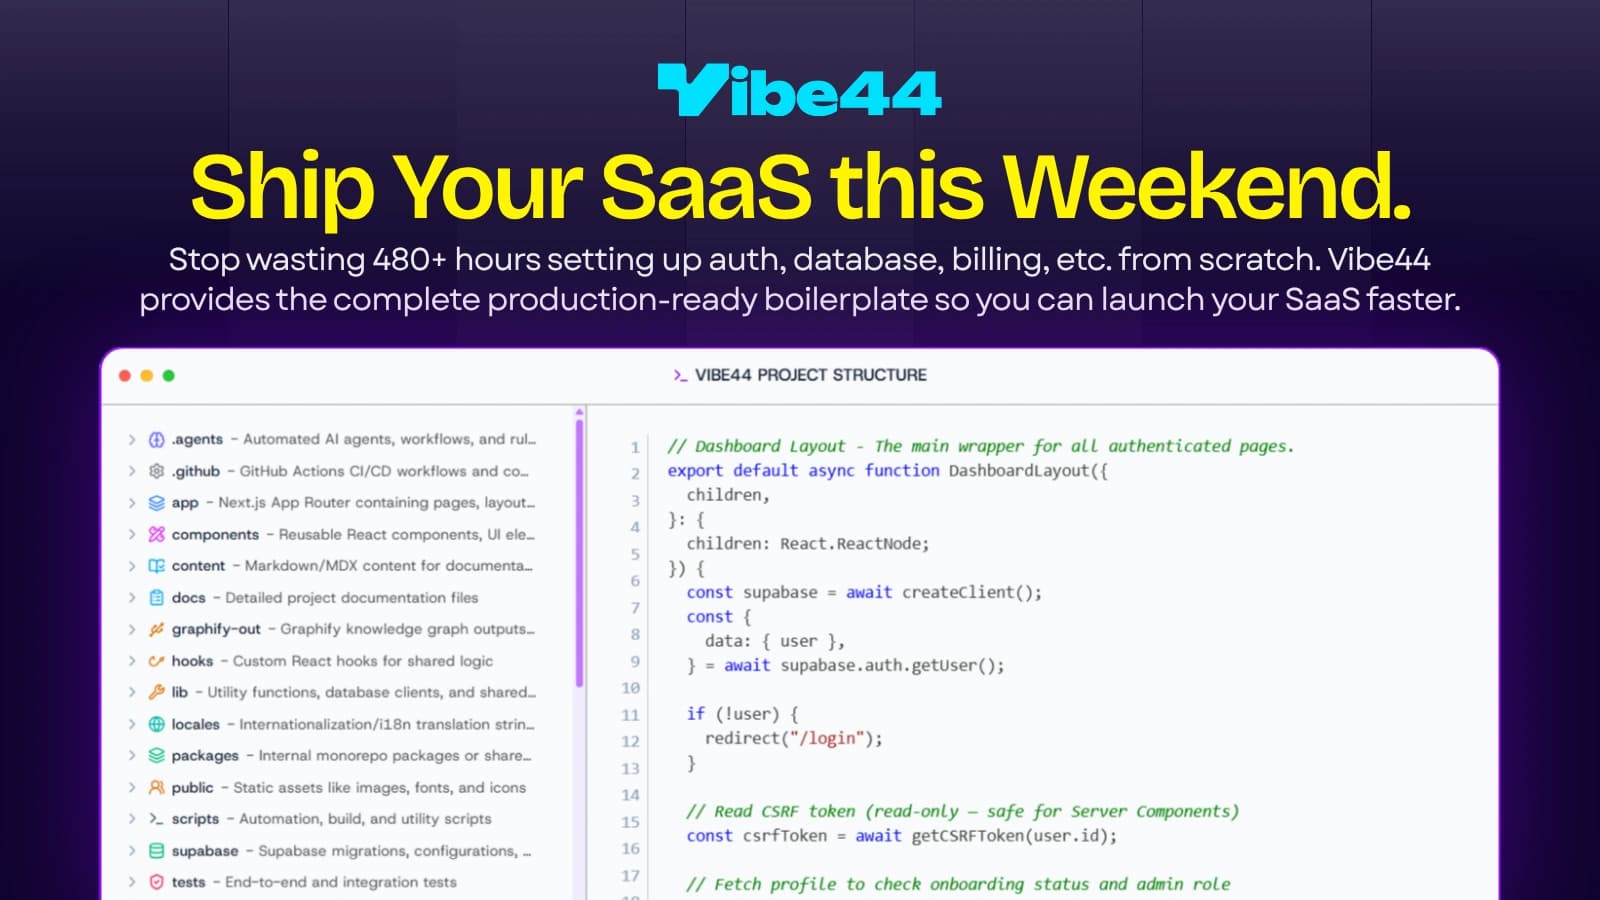
A screenshot of a code editor showing the Vibe44 project structure on the left and a DashboardLayout Next.js component code on the right.
★ FeaturedStartups & Business

How to Ship an AI-powered SaaS in a Weekend? Architecture That Doesn't Fall Over.

The data model you pick on day one decides whether multi-tenancy is a weekend or a quarter. Shared-schema with row-level security scales to thousands of tenants on one database; schema-per-tenant and DB-per-tenant trade that simplicity for operational weight you pay forever. Vibe44 ships shared-schema multi-tenancy by default.

Alap Putatunda

Written by AI &

Alap Putatunda

June 5, 2026Read Full Article
A comparison showing a messy, tangled structure labeled 'BUILD' versus a clean, futuristic, and modular system labeled 'BUY', illustrating the difference between building and buying SaaS infrastructure.
★ FeaturedStartups & Business

Build vs. Buy — What is the Real Cost to Build a Next.js SaaS in 2026?

Building the undifferentiated foundation of a SaaS — authentication, multi-tenant data, billing, security, and observability — costs a senior engineer roughly 480 hours (about 12 weeks) and ~$36,000 of time no customer will ever pay you for. A production-grade Next.js boilerplate ships that same foundation for a $197 one-time license: 32 tables protected by row-level security, Universal Payment and AI adapters, and OWASP Top 10 (2025)-aligned hardening on day one.

Alap Putatunda

Written by AI &

Alap Putatunda

June 3, 2026Read Full Article
A blueprint of a server rack being scanned by a glowing AI eye.
AI & Agents

How to Optimize Your SaaS for ChatGPT, Claude, Perplexity, etc. in 2026?

Building for AI LLMs like ChatGPT, Claude, Perplexity, etc. isn't about keyword density; it's about making your architecture structurally sound for AI consumption. With ChatGPT processing 250–500M weekly queries and capturing ~17% of global digital query share, SaaS founders who don't architect for answer engines are invisible to the next generation of buyers.

Alap Putatunda

Written by AI &

Alap Putatunda

June 13, 2026Read Full Article
A 3D rendering of a checklist with green checkmarks alongside a dashboard showing an upward trending graph, symbolizing production readiness.
Payments & Production

The Production-Readiness Checklist: 27 Things Your SaaS Needs Before Launch!

Shipping a Next.js SaaS to real, paying, hostile users takes more than a green build. This checklist enumerates 27 concrete things — across security and data, payments and billing, and observability and testing — that stand between a demo and production. Vibe44 ships most of the 27 by default, backed by RLS across 32 tables, 900 Vitest unit tests, and 9 Playwright E2E suites.

Alap Putatunda

Written by AI &

Alap Putatunda

June 9, 2026Read Full Article
An illustration of a laptop protected by a blue shield with a padlock and fingerprint scanner, next to a yellow folder with a skull icon, representing OWASP security checks for SaaS.
Auth & Security

The OWASP Top 10:2025 Checklist for SaaS. And How to Actually Cover it?

The OWASP Top 10:2025 is the 8th installment of the list, and it changes the game for SaaS teams: it adds two brand-new categories — A03 Software Supply Chain Failures and A10 Mishandling of Exceptional Conditions — and folds SSRF into A01 Broken Access Control. This post maps all ten risks to a concrete, verifiable Next.js control. Vibe44 ships that coverage out of the box.

Alap Putatunda

Written by AI &

Alap Putatunda

June 1, 2026Read Full Article